Security and trust
Enterprise-grade security. Built in from day one.
Domistra™ is designed for operators who cannot afford to compromise on data security, compliance, or access control.
Data protection and privacy
Your data belongs to you.
All data on Domistra™ is encrypted at rest using AES-256 and in transit using TLS 1.3. Data is stored in region-specific infrastructure.
Compliance
Built to meet the standards that matter.
Domistra™ is designed to meet:
- PIPEDA - Canada's Personal Information Protection and Electronic Documents Act
- GDPR - General Data Protection Regulation (UK and EU)
- PCI DSS - Payment Card Industry Data Security Standard
- SOC 2 - Security, availability, and confidentiality. Readiness documentation available on request.
Roles and access model
Everyone sees what they need. Nothing they do not.
Domistra™ uses an eight-role access model within the PMS, with Admin as the highest operational role. Internal roles: Admin, Manager, Finance, Staff. External roles: Landlord, Tenant, Contractor, Vendor. Access is scoped at the organisation level with row-level security enforced at the database layer.
Account ownership and billing sit in a separate layer entirely - deliberately kept apart from day-to-day PMS operations, so operational access and account control are never tangled together. Every permission is deliberate.
Vendor verification policy
Verified vendors. Not just listed ones.
Vendors on the Domistra™ Marketplace are not anonymous listings. Verified status requires identity verification and licence confirmation where applicable. Property managers can further set their own vendor classifications: approved, preferred, or blocked.
Audit-ready workflows
Every action. On record.
Domistra™ maintains an immutable audit trail across all operational and financial actions. Ticket status changes, lease amendments, financial transactions, document access, and team permission changes are all logged with timestamps and user attribution. Financial exports require 2FA at Business tier and above.
Responsible disclosure
Found a vulnerability? Tell us.
Domistra™ operates a responsible disclosure programme. If you believe you have found a security vulnerability in our platform, report it to us directly before disclosing publicly. We will acknowledge receipt within 48 hours.
Contact: security@domistra.com
We do not pursue legal action against researchers acting in good faith.
Resources
Explore more resources
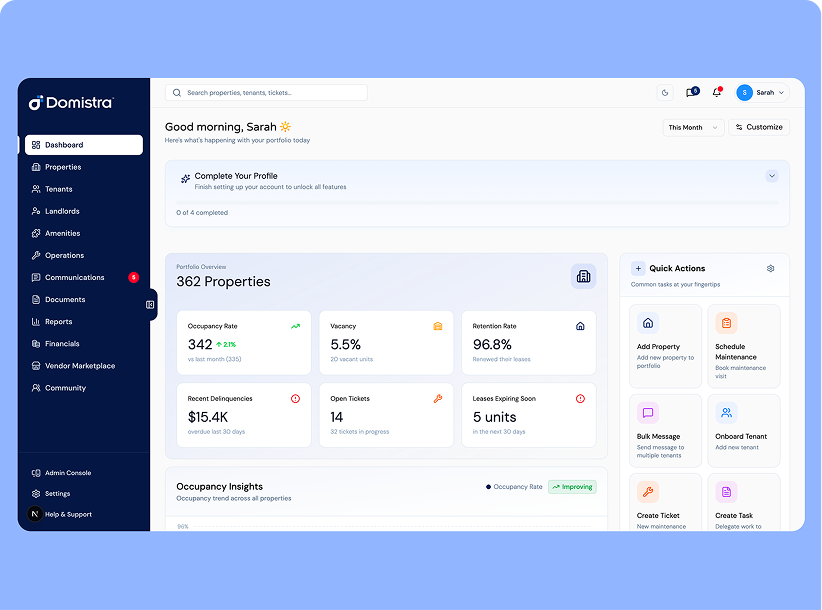
Introducing Domistra™ : Property Management, Connected
Property management touches leases, maintenance, payments, and people, but rarely as one connected system. Here's why we built Domistra differently.
Property Management Doesn't Have a Software Problem. It Has a Coordination Problem.
Property Managers already have plenty of software. What they don't have is a system that connects it. This is why fragmentation, not features, is the real bottleneck.
Beyond Property Management: One Connected Ecosystem
Domistra™ connects property management, payments, vendors, and community into one resident-centric ecosystem, not a bundle of add-ons.